On-Premises Security Intelligence Platform

Your security data
stays on your hardware.
Always.

Viperbyte is the only enterprise cybersecurity platform built for organizations that cannot send their security data to a vendor's cloud. One appliance. Five to seven tools replaced. Full visibility, automated enforcement, and audit-ready compliance evidence — without a single byte leaving your network.

5–7
Tools replaced
by one appliance
0
Bytes of your data
sent to vendor cloud
11
Compliance frameworks
tracked natively
100%
Device coverage
without agents
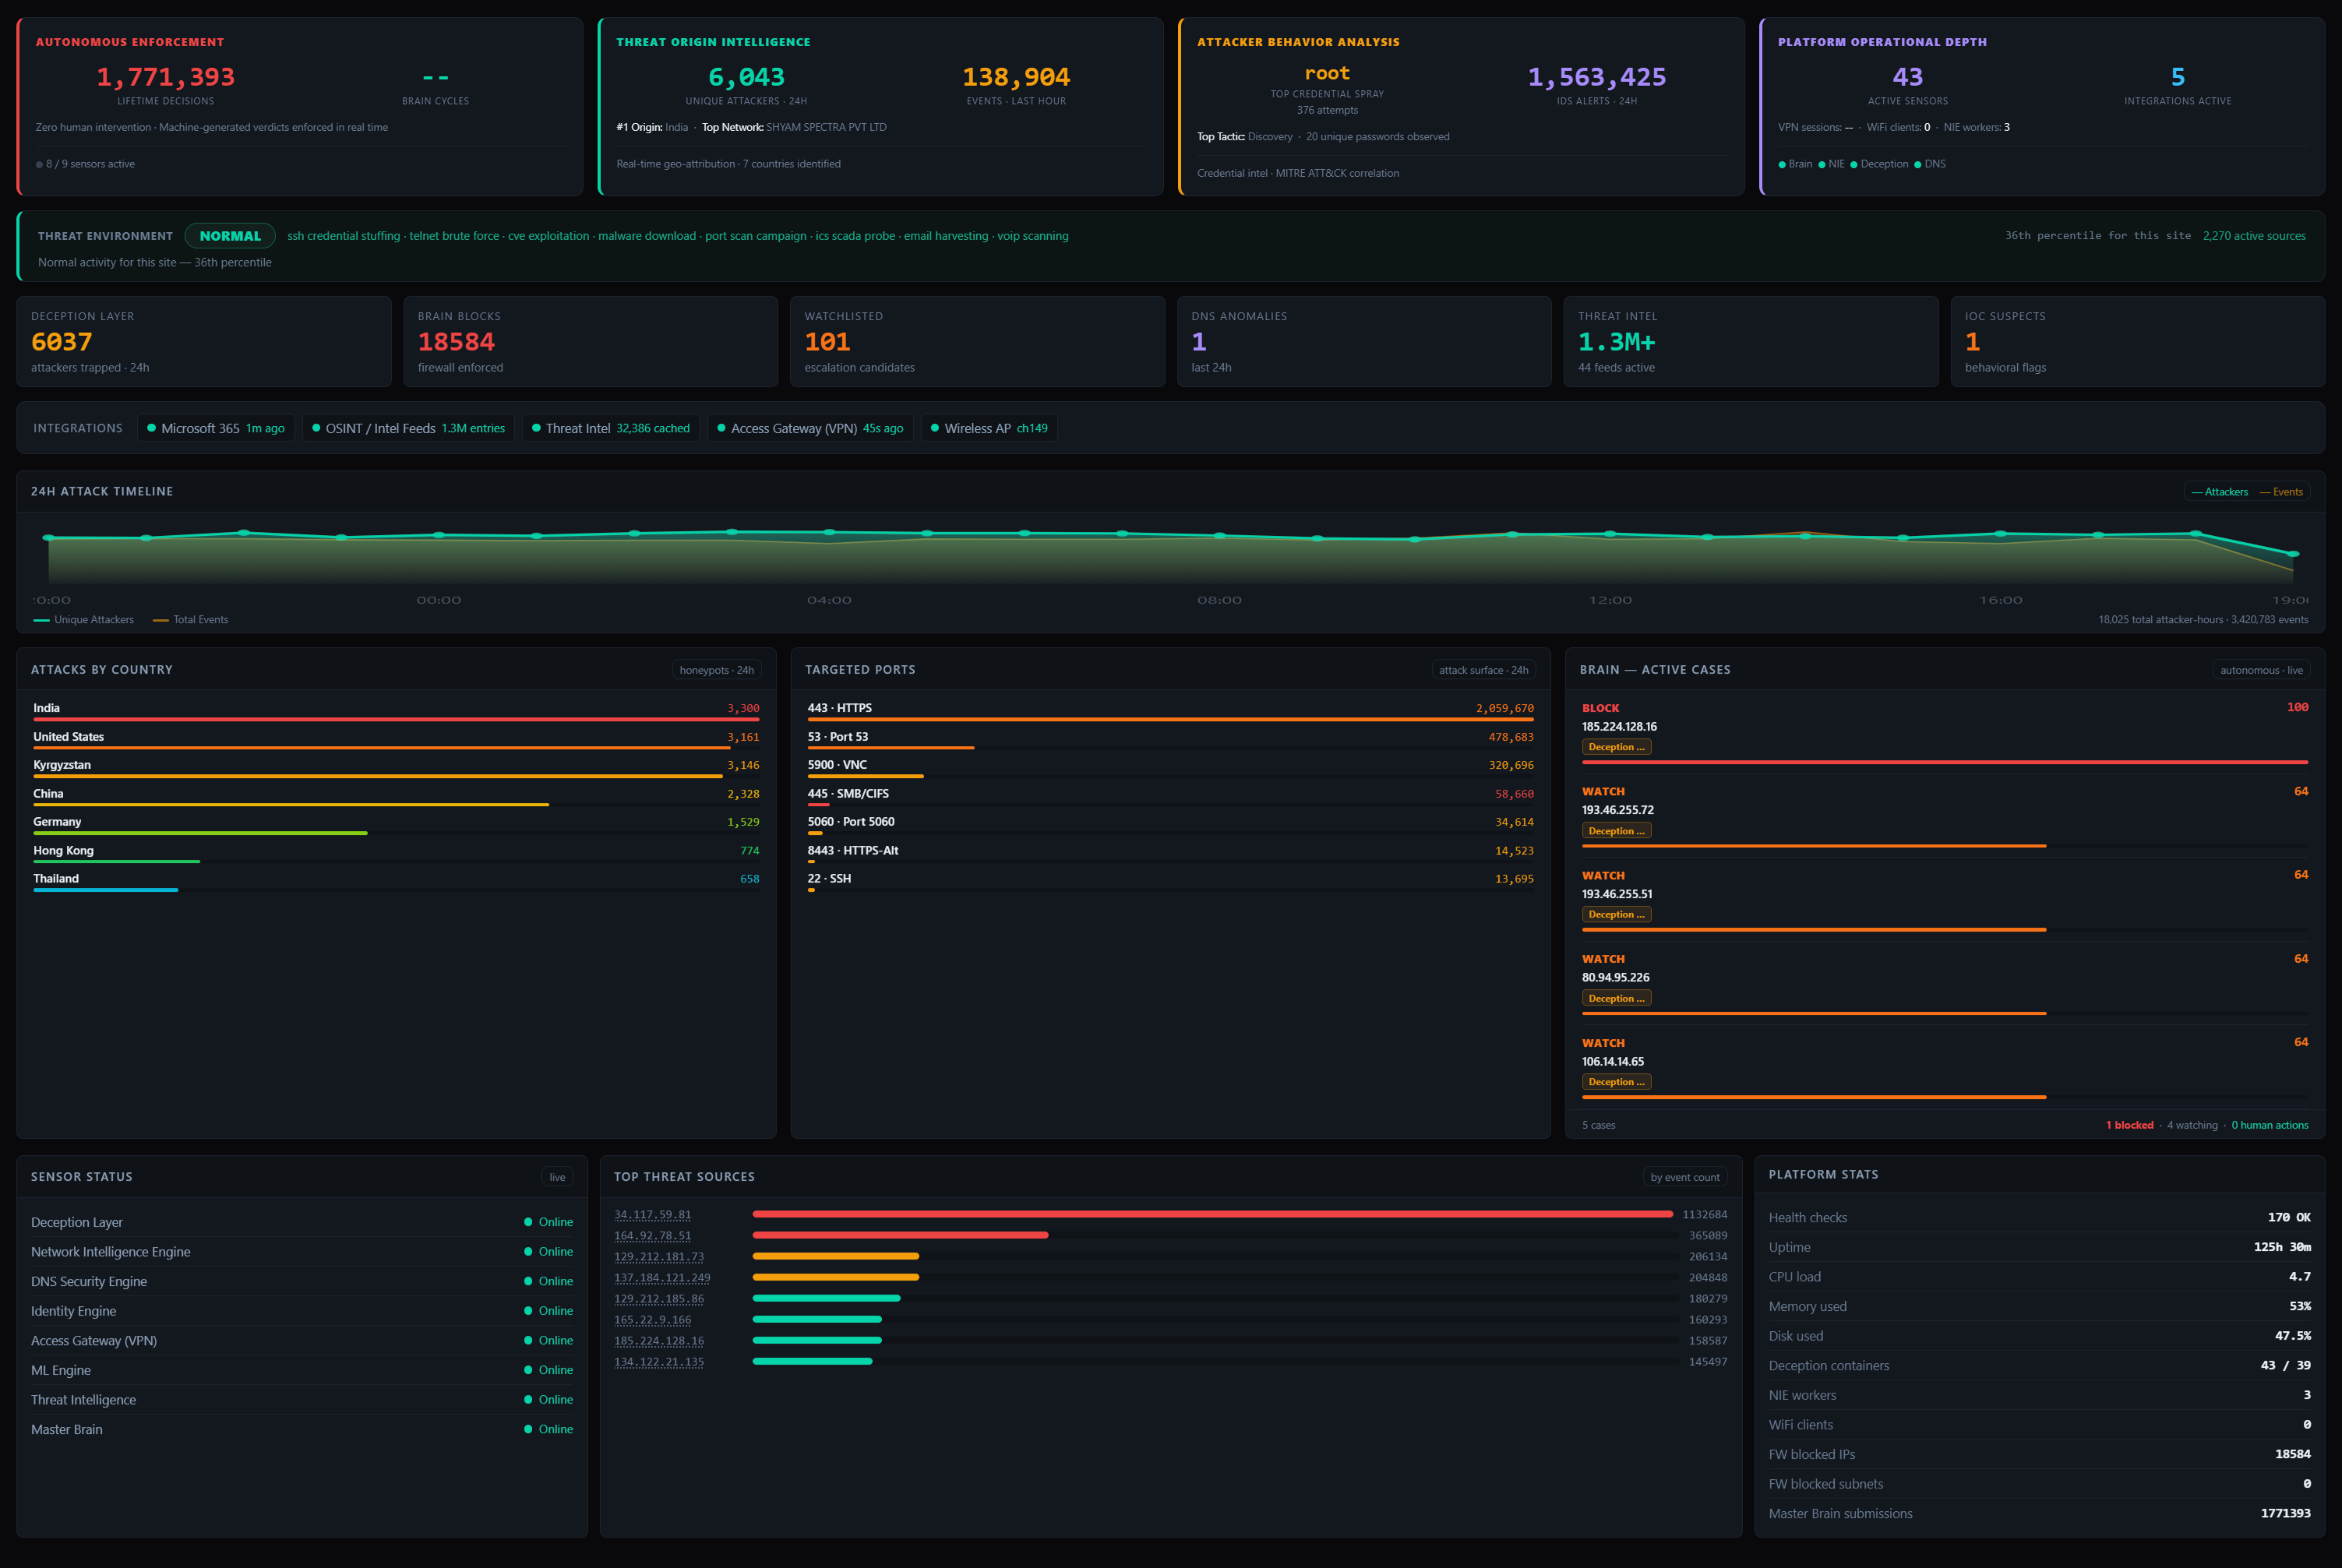
Viper Active Intelligence dashboard — live threat data, entity profiling, autonomous enforcement
Built for compliance-mandatory environments
⚖️ Federal Contractors
🏭 Defense Industrial Base
🏥 Healthcare
🏛️ State & Local Government
🔒 Air-Gapped Networks
🌐 International / GCC
The Problem
Your current security stack
was not built for your requirements.
☁️
Every major SIEM and XDR sends your data to their cloud
Darktrace, Arctic Wolf, Microsoft Sentinel, CrowdStrike Falcon, and Vectra AI all route your security telemetry through vendor infrastructure. For organizations in regulated industries or with data residency requirements, this is a non-starter.
💰
The average security stack costs $230,000–$450,000 per year
SIEM, EDR, NDR, SOAR, compliance tracking, vulnerability management, identity monitoring, and DLP are typically separate tools with separate contracts, separate consoles, and separate vendor relationships.
👥
Those tools assume you have a full SOC team
Enterprise security platforms are engineered for organizations with dedicated security staff. Most mid-market companies don't have that. The tools produce alerts that no one has time to triage.
Typical Mid-Market Security Stack
SIEM (Microsoft Sentinel / Splunk) $48,000/yr
EDR / XDR Platform $36,000/yr
NDR / Network Monitoring $28,000/yr
Compliance / GRC Tool $24,000/yr
Identity Threat Detection $18,000/yr
Deception / Honeypot Layer $15,000/yr
Security Awareness Training $12,000/yr
DLP / Data Loss Prevention $52,000/yr
Typical stack total $233,000/yr
Viperbyte — all of the above $35K–165K/yr
Exact pricing depends on entity count and throughput tier. TCO Calculator →
The Core Differentiator
Your competitors use your
security data as their product.

Every cloud-based security vendor aggregates customer telemetry to train their models, benchmark your posture, and improve their platform. Viperbyte does not. Your data is processed on-premises, by hardware you control, and it never leaves.

Competitors
Your Network
↓
Vendor Cloud
↓
Vendor Data Lake
↓
Model Training
VS
Viperbyte
Your Network
↓
On-Prem Appliance
↓
Local AI Processing
↓
Stays. On. Site.
Cloud-dependency confirmed in privacy policies: Darktrace (Cambridge AI cloud), Arctic Wolf (managed SOC cloud), Vectra AI (cloud-native NDR), CrowdStrike Falcon (Threat Graph cloud), Microsoft Sentinel (Azure-only). Each requires your traffic metadata to route through their infrastructure.
ITAR / CUI data cannot leave your facility
Defense contractors handling Controlled Unclassified Information face legal exposure when security telemetry routes through commercial cloud. Viperbyte was built from the ground up for this constraint.
Your AI model trains on your data, not their aggregate
Viperbyte's behavioral AI learns your specific network baselines. There's no shared model that could leak behavioral signatures from your environment into a competitor's detection logic.
Air-gapped and disconnected operation supported
Viperbyte operates fully on-premises with an optional cloud relay for licensing and updates only — both are optional and can be disabled for truly isolated environments.
Compliance evidence generated locally, stored locally
NIST 800-171, CMMC, SOC 2, ISO 27001, HIPAA, and other framework evidence packages are built on-prem and exported as auditor-ready artifacts. No GRC SaaS required.
Data movement analysis stays on-premises
Viperbyte's Data Flow Intelligence Engine analyzes data movement behavior on-premises — network volume, egress patterns, and cloud app activity — without a single byte of file content leaving your network.
The Hardware
The S2 Appliance.

Installs in your rack or runs as a virtual appliance. Deploys as an active gateway — replacing your existing firewall — or passively alongside your existing infrastructure. Every signal processed locally. No agents, no cloud routing, no vendor access to your data.

Active Intelligence Behavioral Security Appliance S2 VIPER LOCAL AI ACTIVE MONITORING 10G LINK 5K+ ENTITIES PROFILED AUTONOMOUS ENFORCEMENT PWRSPANAIALERT SN VB-S2-000001 MGMTENFORCESPAN 1SPAN 2USBCON
2U Rack Mount
Active / Physical
Active / Virtual
Passive / Physical
Passive / Virtual
1G / 10G Interfaces
Local AI Processing
Zero Cloud Dependency
Compact Variant

Same intelligence.
Palm-size footprint.

For small sites, branch offices, and distributed deployments — the same full intelligence stack in a unit that mounts anywhere. Active gateway or passive alongside existing infrastructure. No rack required.

Platform
Seven integrated engines.
One appliance.

Viperbyte's platform is not a collection of licensed third-party tools repackaged under a new brand. Every engine is purpose-built, shares a unified data model, and feeds a single AI reasoning layer.

🧠
Behavioral Intelligence Engine
Learns the behavioral baseline of every entity on your network — users, devices, printers, IoT sensors — and raises verdicts when behavior deviates. No signatures. No static rules.
Replaces: SIEM + UEBA
🕸️
Network Intelligence Engine
Deep packet inspection of all network flows. Detects lateral movement, data exfiltration, command-and-control beaconing, and anomalous DNS behavior without routing traffic externally.
Replaces: NDR / Network Detection
🎯
Deception Layer
Distributed honeypots deployed across every VLAN. Any interaction with a deception asset is an unambiguous indicator of compromise — zero false positives. Rare in this price segment.
Replaces: Standalone Deception Platforms ($15K–$60K/yr)
👤
Identity Engine
Unified identity profile for every user: Active Directory, Microsoft 365, VPN sessions, Wi-Fi authentication, workstation logins, and behavioral patterns — merged into a single timeline.
Replaces: Identity Threat Detection (ITDR)
📋
Compliance Engine
Continuously maps your security posture against 11 frameworks. Generates auditor-ready evidence packages on demand — not just a dashboard, but actual documentation your auditor can cite.
Replaces: GRC Platforms + Manual Evidence Collection
⚡
Enforcement Engine
Automated and admin-configurable enforcement: firewall blocks, EDR isolation triggers, Wi-Fi deauthentication, VPN termination. Five enforcement tiers, from alerting to autonomous containment.
Replaces: SOAR + Manual Incident Response
📤
Data Flow Intelligence Engine
Detects exfiltration by anomaly, not content scanning. Covers every device on the network, including those no DLP agent can reach. When Microsoft 365 is connected, network-layer signals are corroborated against cloud file activity.
Replaces: DLP / Data Loss Prevention ($50K–$150K/yr)
Compliance Native
Compliance evidence generated,
not just tracked.

Most compliance tools show you a dashboard of what's passing and failing. Viperbyte generates the actual evidence packages auditors require — timestamped logs, control mappings, and narrative reports — from the data it's already collecting for security purposes.

📄
Audit-ready report generation
Generate control evidence packages for NIST AU-7, CM-2, and other controls directly from the platform — formatted for auditor review, not just internal dashboards.
🔗
Integration-aware posture scoring
Viperbyte knows which of your integrations (EDR, MDM, SAT) close which controls. Posture is honest — a control is only marked closed when the technology that closes it is verified active.
⏱️
Continuous, not point-in-time
Every control is monitored in real time. When a configuration drifts out of compliance, the platform flags it immediately — not at the next annual assessment.
📤
Data movement analysis, built in
Viperbyte's Data Flow Intelligence Engine closes data movement controls natively — no additional tool, no additional cost. Content-aware coverage expands automatically when Microsoft 365 is connected.
Supported Frameworks
NIST 800-171
CUI Protection
86% closeable with integrations
CMMC Level 2
DoD Contractors
91% closeable
SOC 2 Type II
Trust Services
74% closeable
ISO 27001
International
81% closeable
HIPAA
Healthcare
88% closeable
GovRAMP Low
Federal Cloud
79% closeable
Also includes: PCI-DSS, CCPA, GDPR, FISMA, CMMC Level 3. Coverage percentages shown are with integrations (MDM, EDR, SAT) active. Genuine gaps exist where Viper cannot manufacture compliance — those are shown honestly.
Deployment
Running in days, not months.

No agent rollout. No multi-month implementation project. No professional services team living on-site for six weeks.

1
Appliance Deployed
Physical or virtual. Active mode replaces your existing gateway — full enforcement from day one. Passive mode sits alongside existing infrastructure — zero network changes required.
2
Entities Discovered
Every device, user, and network identity is automatically discovered and fingerprinted. Active Directory and Microsoft 365 sync enriches identity profiles within hours.
3
Baselines Learned
The behavioral AI learns what normal looks like for your specific environment over 7–14 days. No pre-configured rule sets. No vendor-defined "typical" behavior substituted for yours.
4
Automated Enforcement
Once baselines are established, the platform flags, escalates, and (optionally) enforces automatically. You configure how much autonomy the system has — from advisory to autonomous containment.
Comparison
How Viper compares
to alternatives.
Capability Viperbyte Darktrace Arctic Wolf CrowdStrike XDR Microsoft Sentinel
Data stays on your hardware ✓ — — — —
No per-agent licensing required ✓ — — — —
Built-in deception / honeypot layer ✓ Add-on — — —
Compliance evidence generation ✓ — Partial — Partial
CMMC / ITAR ready (on-prem) ✓ — — — —
MSP channel — exclusive reseller model ✓ Limited Limited Limited Limited
Agentless device coverage ✓ ✓ — — —
Behavioral AI / anomaly detection ✓ ✓ ✓ ✓ ✓
Mid-market pricing (<1,000 endpoints) ✓ — MDR only — Complexity cost
Single-pane management (no SIEM required) ✓ ✓ — — —
Data movement / DLP monitoring ✓ Network only — Agent required Purview add-on (E5)

Based on publicly documented product capabilities and privacy policies as of 2026. Subject to change as vendor offerings evolve.

Who We Serve
Purpose-built for organizations
where security data residency matters.
🏭
Defense Industrial Base Contractors Organizations handling CUI must comply with CMMC before pursuing DoD contracts. Viperbyte's on-prem architecture satisfies DFARS 252.204-7012 without routing sensitive data through commercial cloud.
🏥
Healthcare Organizations HIPAA-covered entities face OCR scrutiny over where PHI-adjacent security data is processed. On-prem deployment eliminates cloud BAA complexity while generating the audit evidence HHS requires.
⚡
Critical Infrastructure Operators Utilities, energy, water, and transportation operators with OT/ICS environments need passive, agentless monitoring that doesn't require touching operational systems or routing OT telemetry externally.
⚖️
Legal, Financial & Professional Services Client confidentiality obligations (attorney-client privilege, fiduciary duty) create legal liability when security tools can access privileged communications. Local processing eliminates vendor exposure.
"We evaluated three cloud-based SIEM platforms before realizing none of them could satisfy our DFARS requirements. Viperbyte was the first platform that actually understood the problem — and solved it without requiring us to accept cloud data routing."
IT Director
Defense Subcontractor — 340 Employees
🏛️
State & Local Government SLTT agencies face increasing ransomware targeting with constrained budgets. Viperbyte replaces multiple point solutions at a fraction of the cost while meeting CISA's cross-sector cybersecurity performance goals.
🔐
Federal Contractors (Non-FedRAMP paths) For contractors where FedRAMP-authorized SaaS isn't mandated, on-premises deployment provides a compliant alternative that keeps sensitive program data entirely within the contractor's boundary.
🌐
Air-Gapped / SCIF Environments Viperbyte's core security functions operate without cloud connectivity. Licensing and signature updates use an optional relay — which can be disabled entirely for completely isolated environments.
"The combination of CMMC evidence generation and on-prem data sovereignty made Viperbyte the only platform we could deploy without a legal review and a data processing agreement with a third-party cloud vendor."
CISO
Federal Systems Integrator
🌍
GDPR-Regulated Organizations Organizations subject to GDPR face significant complexity when security tools transfer personal data to US-based cloud infrastructure. On-prem processing eliminates cross-border transfer risk entirely.
🏗️
GCC & MENA Market Gulf Cooperation Council countries with national data localization requirements need security platforms that can operate within-border. Viperbyte's architecture was designed for this from day one.
🏦
International Financial Institutions Banking regulators in multiple jurisdictions (ECB, FCA, SAMA, MAS) impose data residency requirements on financial institutions that make cloud-based security telemetry problematic.
"Data sovereignty is not a checkbox for us — it is a regulatory requirement. Viperbyte is the first platform we evaluated that treated it as an architecture decision, not an afterthought."
Head of Information Security
Regional Financial Institution — GCC
MSP Channel
Viper delivered by your team.
At your margin.

Viper is sold exclusively through a managed service provider channel. MSPs resell and manage Viper for their clients, set their own service pricing, and retain 30–40% margin below MSRP. We don't compete with you for end customers.

01
Your service, your client relationship
You manage Viper for your clients under your managed service offering. Your contract, your SLA, your relationship. Viper is the platform you deliver.
02
Per-client isolation architecture
Every client deployment is a fully isolated on-premises instance. Zero shared infrastructure. Zero cross-client data exposure. Zero liability from a neighbor's breach.
03
Recurring revenue model
Annual platform licenses plus consumption-based metering for AI enforcement actions. Predictable base revenue with upside from high-activity clients.
04
Compliance as a billable service
Viperbyte generates compliance evidence. You deliver it as a governance advisory service. New billable hours on top of the platform fee — using work the platform already did.
Build a Viper Practice
Small Client
~150 entities
~$5,100/mo
Mid-Market Client
~400 entities
~$9,100/mo
Enterprise Client
~800 entities
~$15,600/mo
What a Viper Practice Adds to Your Book
5 managed clients +~$550K ARR
10 managed clients +~$1.1M ARR
20 managed clients +~$2.2M ARR
Platform fees scale with entity count and throughput tier — use the TCO Calculator for a client-specific number. Channel pricing and partner margin structure are shared with approved MSPs. Apply to partner →
Resources
Go deeper.

Security that works for
your requirements.

On-prem. Agentless. Compliance-native. See how Viperbyte replaces your current stack and closes your open framework gaps.